Editor’s Note: New York’s $33 million consent order against Skandinaviska Enskilda Banken converts a Baltic monitoring backlog into a U.S. regulatory finding, and much of its evidence comes from the bank’s own internal audits. The order describes alert queues that built up across SEB’s Estonian, Latvian and Lithuanian subsidiaries, alerts often closed on outdated standardized forms, screening decisions with no recorded reason and suspicious activity reports that auditors could not check for timeliness.
For cybersecurity, data privacy, regulatory compliance and information governance professionals, those are records problems as much as monitoring problems, because the artifacts a monitoring program produces about itself became findings years later. For eDiscovery practitioners, the order’s reservation of conduct not disclosed in SEB’s written submissions, set beside the department’s July 2026 Swedbank penalty, shows how closely a settlement’s reach can track what a bank put in writing.
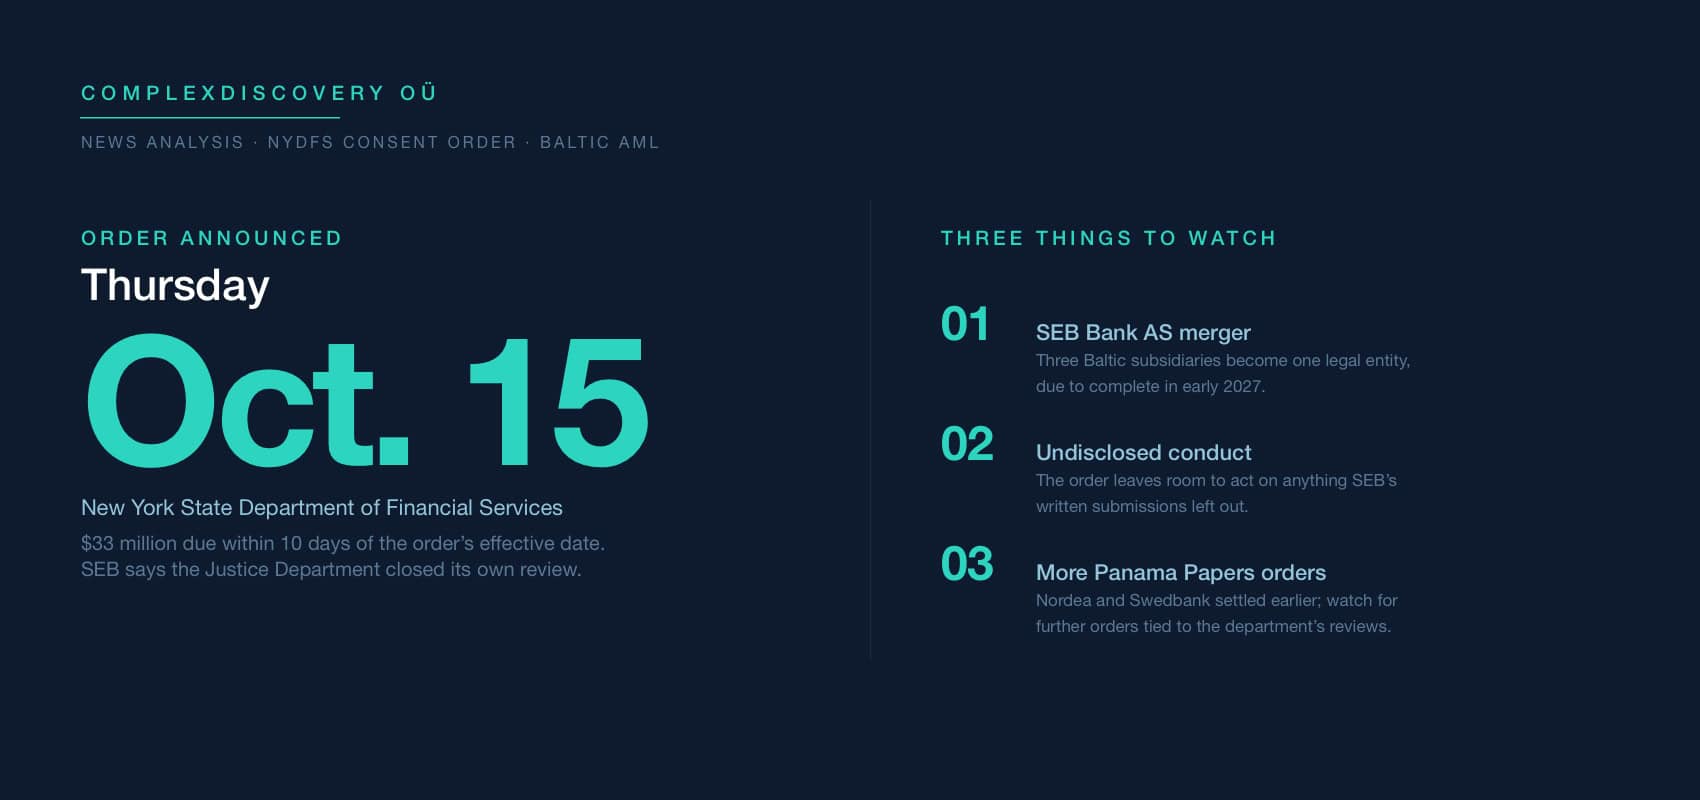
Watch whether the department announces further orders tied to its Panama Papers reviews, and follow SEB’s merger of its three Baltic subsidiaries into SEB Bank AS, due to complete in early 2027.
Content Assessment: New York fines SEB $33 million, citing the bank's own audits of its Baltic units
Information - 92%
Insight - 91%
Relevance - 90%
Objectivity - 90%
Authority - 88%
90%
Excellent
A short percentage-based assessment of the qualitative benefit expressed as a percentage of positive reception of the recent article from ComplexDiscovery OÜ titled, "New York fines SEB $33 million, citing the bank's own audits of its Baltic units."
News Analysis – Governance Beat
New York fines SEB $33 million, citing the bank’s own audits of its Baltic units
ComplexDiscovery OÜ Staff
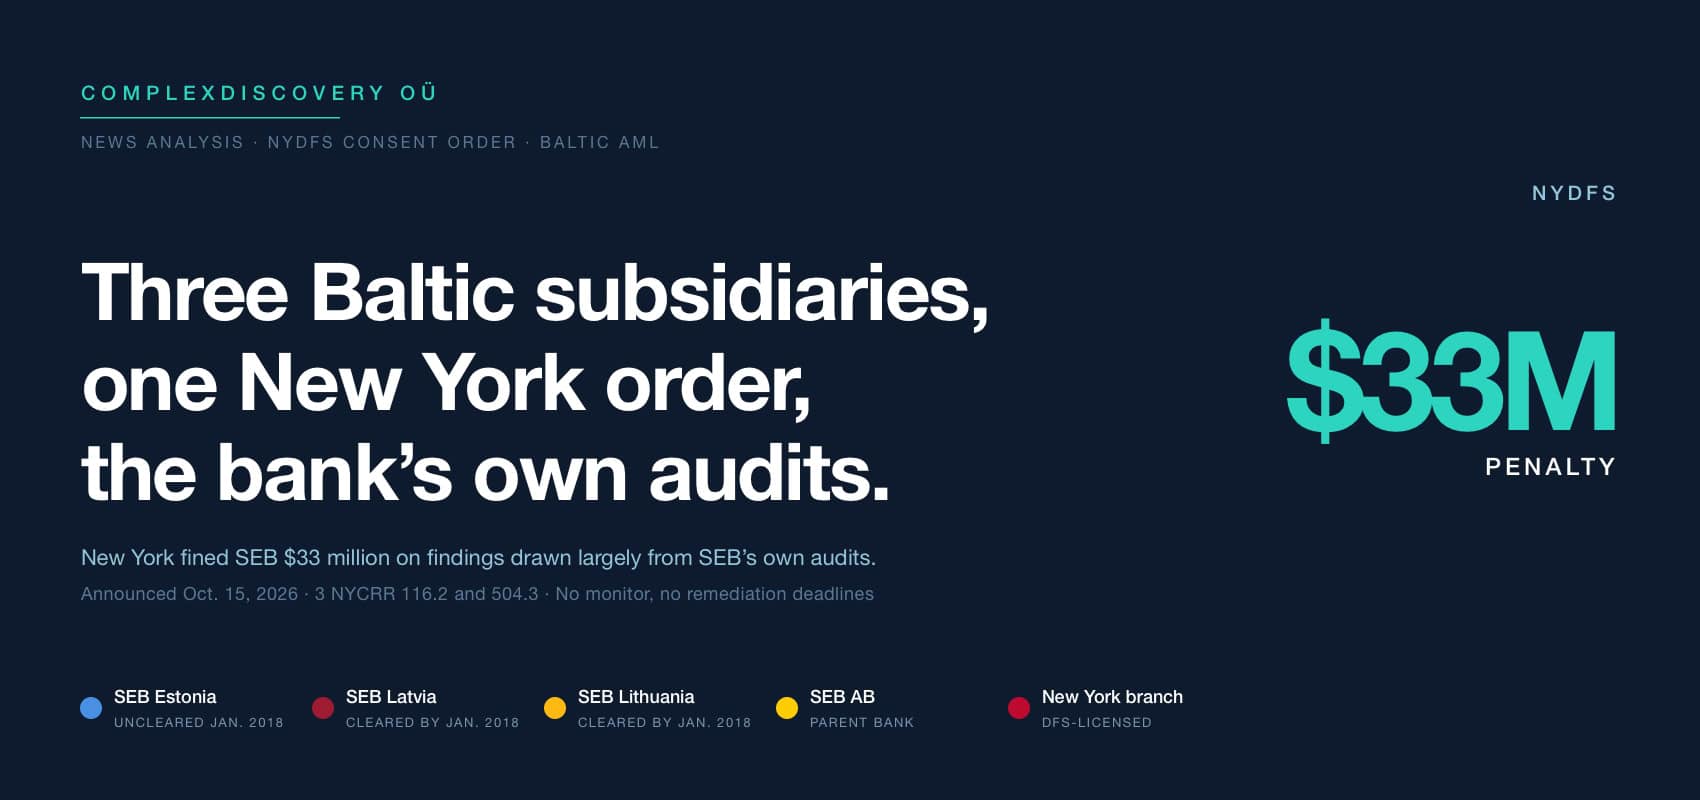
New York’s financial regulator fined Skandinaviska Enskilda Banken $33 million on Oct. 15 over money laundering controls, in an order that leans heavily on the Swedish bank’s own audits of its Baltic subsidiaries.
The backlog named in the announcement formed in Estonia, Latvia and Lithuania, not in New York. According to the consent order, a 2018 SEB audit found the bank’s alert processing substantially backlogged at all three Baltic subsidiaries. By January 2018, the Latvian and Lithuanian units had cleared theirs, but the Estonian unit still had not.
The New York State Department of Financial Services (DFS) said Skandinaviska Enskilda Banken AB and its New York branch agreed to the penalty to resolve an investigation into the bank’s anti-money laundering program. “The Department will hold entities accountable that fail to meet those standards,” acting Superintendent Kaitlin Asrow said in the department’s release. The 28-page order finds that SEB did not keep an effective program running in its Baltic subsidiaries from 2015 through 2019. It cites two regulations, 3 N.Y.C.R.R. § 116.2 for the due diligence failures and 3 N.Y.C.R.R. § 504.3 for an inadequate transaction monitoring system.
The settlement terms center on the payment. SEB must pay within 10 days of the order’s effective date, and it may not claim a deduction or credit for the penalty against any U.S. federal, state or local tax, or seek reimbursement through insurance. The settlement provisions impose no independent monitor or consultant and set no remediation deadlines. The department says it recognizes the remediation SEB has already carried out.
What the order says about the backlog
Those terms resolve the case, while the findings explain it and locate the backlog more precisely than the release does. The release says SEB’s transaction monitoring systems were backlogged, allowing transactions to “evade timely review for money laundering and sanctions risks.” In the order, the Baltic subsidiaries ran a system called Financial Crime Risk Management, which checked the previous day’s transactions against predefined money laundering scenarios and raised alerts. The backlog was in working those alerts. It seemed to clear for a period in 2017, the order says, before returning later that year at all three subsidiaries.
Other failures sat upstream of the queue. A 2018 internal audit found the subsidiaries had not ensured proper controls on the data delivered into the system. Between July 6 and Aug. 10, 2017, the system generated no new alerts for Estonia at all. SEB Estonia’s compliance team concluded that an alert-generation process had been started but never completed, and SEB later reviewed that period’s transactions manually.
The record of how alerts were closed was weak too. A 2018 audit of SEB Estonia found that alerts for politically exposed persons rested on an incorrect scenario matrix and that staff closed them as they arrived, sometimes up to 100 a day. When SEB Estonia closed alerts, it often used outdated standardized forms and sometimes recorded an investigation that had not happened. A second tool, SafeWatch, screened payments in real time. The 2018 audit found it did not document why staff released a payment, assigned it to the compliance team or blocked it, and SEB did not record those reasons anywhere else. When SafeWatch was down in Estonia and Latvia, payments went through without sanctions screening and were reviewed manually afterward.
How Baltic queues became a New York exposure
All of those failures sat inside the three Baltic subsidiaries, and a section of the order explains how they still reached New York. The parent, SEB AB, set group-wide anti-money laundering controls that applied to the Baltic subsidiaries and the New York branch alike. About $300 million in transactions originating at the Baltic subsidiaries moved through the New York branch between 2006 and 2019, and $2.5 million of that fell between 2015 and 2019.
Dollar clearing was the larger channel. The order says one New York bank licensed by the department, which it does not name, processed $144 billion of transactions with the Baltic subsidiaries between 2015 and 2019. A second U.S. institution, also unnamed, cleared $131 billion involving them between 2017 and 2019. The order reports those figures separately and for different periods. Through those channels, it says, the elevated risk in the Baltics was “imported into the U.S. financial system.”
The customer files were part of that risk. SEB’s 2015 internal audits found the Baltic subsidiaries had not updated know-your-customer information for 64 percent of legal entity clients, and 42 percent of the files SEB audited lacked beneficial ownership information. For correspondent banks, the order says SEB applied only simplified due diligence to several high-risk partners, kept deficient files on them, calculated their risk incorrectly and failed to update the governing procedures. It identifies those counterpart banks only by number. The release’s reference to deficient client files tracks that passage, and neither document charges a separate recordkeeping violation.
A case assembled from the bank’s own paperwork
What the order draws on instead, again and again, is SEB’s own internal review work. Its transaction monitoring section runs 12 numbered paragraphs, and eight of them attribute their findings to an SEB audit or to SEB’s own compliance staff. The bank made the same point in its announcement. “The review is to a large extent based on the bank’s own internal controls and conclusions regarding the former processes in the Baltics during the relevant period,” Cecilia Wolrath Ekenbäck, SEB’s head of group compliance, said.
That internal record also shows where reporting broke down. SEB auditors concluded they could not tell whether SEB Latvia filed suspicious activity reports on time or at all. In SEB Lithuania, auditors could not check whether filings were complete and on time, because the reports sat in separate sources. Each subsidiary assigned a single employee to submit the reports and run the related investigations, without quality control checks.
European supervisors acted on SEB’s Baltic controls years before New York’s order. The order itself says Swedish, Estonian and Latvian authorities flagged deficiencies and issued fines in 2019 and 2020. On June 25, 2020, Sweden’s Finansinspektionen gave SEB a remark and an administrative fine of 1 billion Swedish kronor. The same day, Estonia’s Finantsinspektsioon fined AS SEB Pank 1 million euros for four breaches running from late 2017 to September 2019. The first one it listed was a breach of the requirement to register and retain data; the others covered identifying beneficial owners, monitoring business relationships and reporting suspicions.
Three Nordic banks, one line of New York reviews
New York’s own interest in those Baltic files began with a different set of records. The DFS release ties the case to reviews the department opened after the 2016 Panama Papers leak of Mossack Fonseca law firm records. The order itself does not mention the leak, and its findings concern Baltic customers and correspondent banks.
SEB follows two other Nordic banks whose DFS settlements the department’s releases also tie to the leak, though the Swedbank case turned on different conduct. In August 2024, DFS fined Nordea Bank Abp $35 million, citing among other failures weak safeguards at its former Baltic branches. In July 2026, the department fined Swedbank $50 million for failing to cooperate fully, finding that Swedbank “intentionally excluded its Baltic subsidiaries from its production to the Department.” SEB’s order, by contrast, gives weight to the bank’s “timely and appropriate responses to requests for information.”
SEB said the U.S. Department of Justice also closed its own review with no action, ending the bank’s U.S. matters on its historical anti-money laundering measures. The DFS order says it binds no federal agency, no other state agency and no law enforcement authority. It also preserves the department’s ability to act on conduct not disclosed in the written materials SEB submitted.
Where monitoring and discovery teams can start
That reservation ties the reach of the settlement to what the bank put in writing. The department commits to no further action on the conduct the order describes, provided SEB complies, but anything the bank’s submissions left out stays open. Swedbank’s penalty turned on what its production omitted. eDiscovery teams scoping a regulator’s request across a multinational group can confirm that foreign subsidiaries were actually searched, rather than assuming the licensed branch defines the universe of responsive records.
The same logic runs through the monitoring records themselves. For compliance and information governance teams, the order works as an inventory of the evidence a monitoring program generates about itself. Alert queues and their age, closure forms, screening decisions, downtime periods and suspicious activity report logs all appear in it as findings. Teams can treat backlog counts as records a regulator may read years later, and can require a case-specific written reason for each alert closure instead of a template.
Part 504 already points that way. When the department adopted the rule in 2016, it set an effective date of Jan. 1, 2017, and said monitoring programs must include protocols for investigating alerts, to the extent applicable. Those protocols also set out how the institution decides which alerts lead to a filing or other action, who makes that decision and how the process is documented. It also said institutions must keep the data supporting each annual compliance certification for five years. The department’s current guidance adds that it may request those records at any time.
The entities named in the order are also changing shape. Estonia’s Finantsinspektsioon said on May 22 that the European Central Bank had approved combining SEB’s three Baltic subsidiaries into one legal entity, SEB Bank AS, with Latvian and Lithuanian operations continuing as branches. The merger is due to complete in early 2027, and the authority said anti-money laundering supervision will stay with each country’s local supervisor.
If a regulator can build much of a $33 million case from audit reports a bank wrote about itself, how many organizations know what their own monitoring records would show if someone read them years after the events they describe?
News sources
- New York State Department of Financial Services Secures $33 Million Penalty with Skandinaviska Enskilda Banken AB for Inadequate Anti-Money Laundering Controls and Transaction Monitoring Compliance Failures (New York State Department of Financial Services)
- NYSDFS Enforcement Action: October 15, 2026: Consent Order Issues to Skandinaviska Enskilda Banken AB (New York State Department of Financial Services)
- Transaction Monitoring Certification (Reg 3 NYCRR 504) (New York State Department of Financial Services)
- New York State Department of Financial Services Secures $50 Million Penalty from Swedbank for Withholding Information from Investigators (New York State Department of Financial Services)
- Superintendent Adrienne A. Harris Secures $35 Million Settlement with Nordea for Significant Compliance Failures and Inadequate Diligence Over High-Risk Correspondent Banks (New York State Department of Financial Services)
- SEB receives remark and administrative fine of SEK 1 billion (Finansinspektionen)
- AS SEB Pank is fined for breaches of the anti-money laundering rules (Finantsinspektsioon)
- SEB got permission to merge in the Baltics (Finantsinspektsioon)
- New York Codes, Rules and Regulations, Part 504, Section 504.3: Transaction Monitoring and Filtering Program Requirements (Justia)
- SEB reaches a resolution with DFS, concluding US authorities’ reviews of the bank’s historical processes (SEB via Inderes)
- SEB fined €1 million over money-laundering prevention deficiencies (ERR News)
- New York’s New AML Rule: Strategic Considerations and Alternatives (Arnold & Porter)
- NYS Banking Regulator’s Requirements for Transaction Monitoring and Filtering (Harvard Law School Forum on Corporate Governance)
Assisted by GAI and LLM Technologies
Additional reading
- OFAC’s ICC General License 14 has no stated expiration date, but does it reach eDiscovery services?
- Cooley and Google Cloud are building a court-filing redaction agent without a published error rate
- Relativity’s 2028 Server exception meets a Riyadh deployment outside its cloud region table
- ENISA Threat Landscape 2026 finds DDoS leads incident counts while ransomware stays most impactful in the short term
- Cyber Resilience Act reporting starts Sept. 11 on an unfinished platform
- Europe’s draft cloud rule would put vendor ownership in the audit file
- The eight-hour clock starts today: EU e-evidence orders now land on covered U.S. providers’ EU addressees
- California’s AI Transparency Act arrives alongside Europe’s Article 50
- Federal magistrate judge treats LinkedIn’s Relativity aiR workflow as TAR
- One benchmark, three directions: 2026 legal rates rise, flatten and fall at once
- Confidence cools, commitment holds: full results from the 1H 2026 eDiscovery Business Confidence Survey
- Complete look: ComplexDiscovery OÜ’s 2025 to 2030 eDiscovery market size mashup
- The workstream of eDiscovery: Considering processes and tasks
Source: ComplexDiscovery OÜ
ComplexDiscovery’s mission is to enable clarity for complex decisions by providing independent, data‑driven reporting, research, and commentary that make digital risk, legal technology, and regulatory change more understandable for practitioners, policymakers, and business leaders.